You shipped it.Got a new app?

Hackers don't pick you. They try every app they find.Before you pay for an app, check it.

They scan the internet all day for AI keys, passwords and customer data left in the open.1 Paste your link and see what they'd find. Free.If the app leaks, strangers can see your customers' names and phone numbers. Check what's open to anyone, free. No technical skills needed.

Check your app free

  1. Sign in
  2. Confirm

Is the app only on your phone? Ask your builder for its web link.

We only look. We never break in. Only check apps you own, or have permission to check.An app built for your business? You can check it.

The 30-second story

Works with Lovable, Bolt, v0, Replit, Cursor and Claude Code apps. Someone built your app? Check it before you pay →Built it yourself? →

See what happens next

The moment you go live

You hit publish. Now anyone can reach it.Your builder hit publish. Now anyone can reach it.

Your users, your client, and people nobody invited.

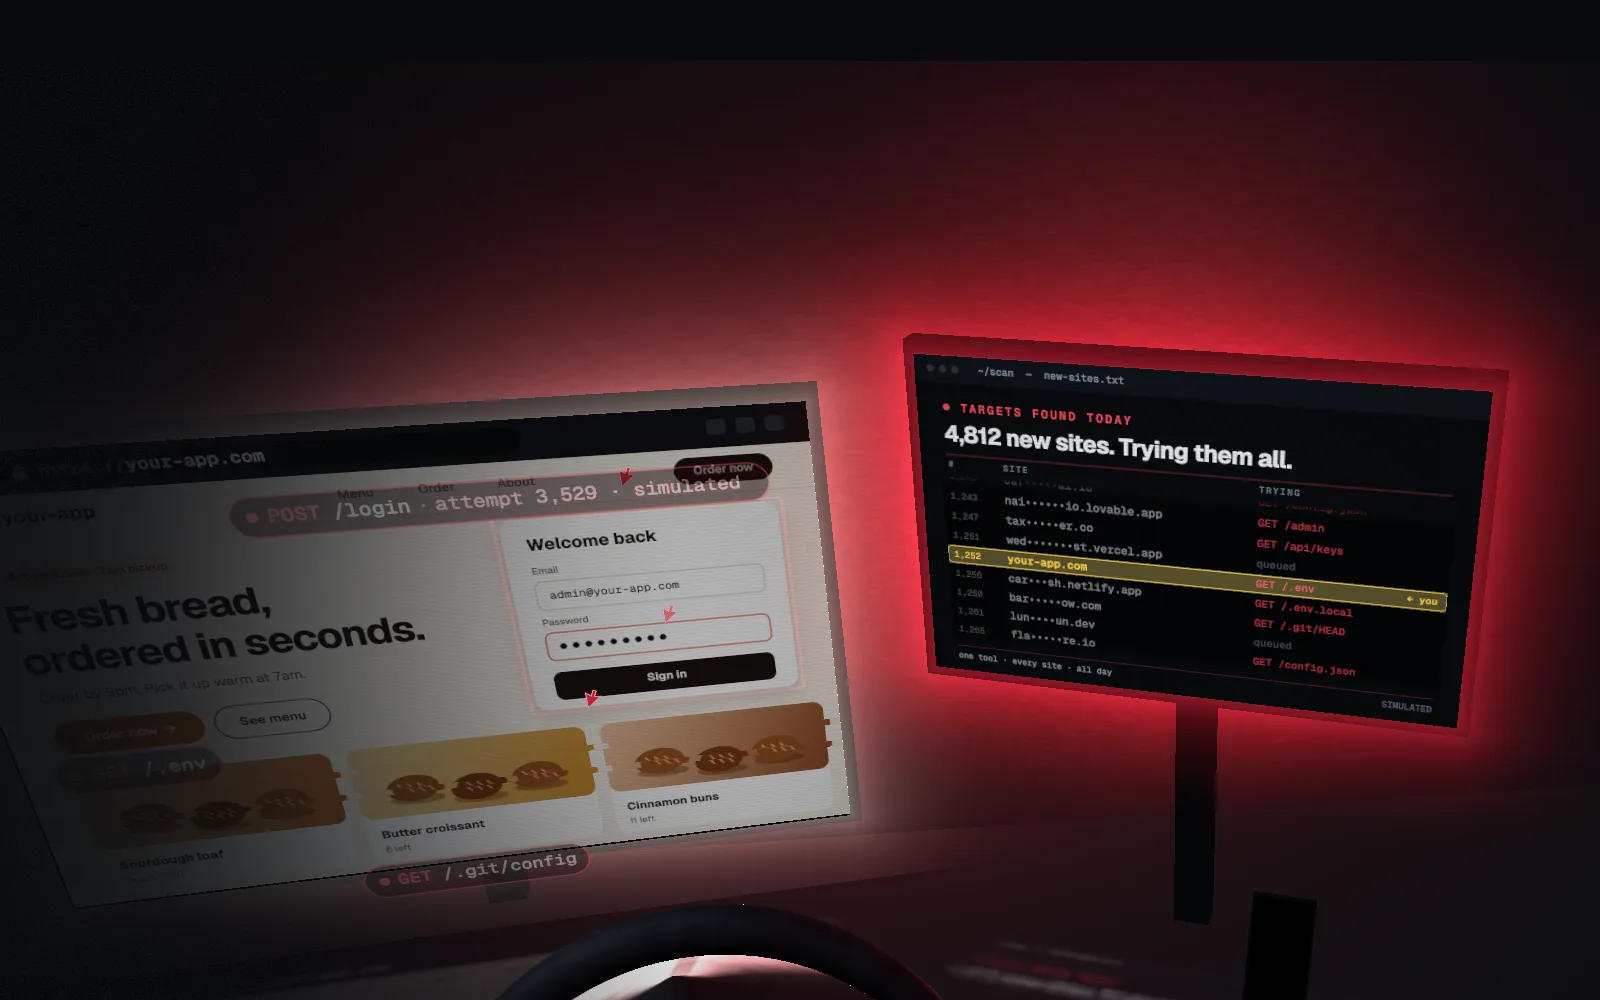
Over a hacker's shoulder: your site, live on his screen, with the first request coming in.

Minutes later

Within minutes, hackers find it.

Nobody sits there typing. Their tools scan the internet nonstop and try every new site they hit.1

≈2 safter a brand-new website went online, it was asked for its password file and its code history. SANS ISC, Aug 20232

The hacker's screen: a list of thousands of new sites, with yours highlighted as one of them.

What they try

They try every door you forgot to lock.

Your AI key, left where any visitor can copy it. Your passwords file. Your app's code. Your customers' data. (.env, .git, API keys, your database)

ExampleExample app. Your results come from your own check.

  • .env→ keys & passwords
  • .git→ your code
  • AI key→ your bill
  • database→ your customers

110,000websites had their password files stolen by one hacking operation in 2024. Palo Alto Unit 423

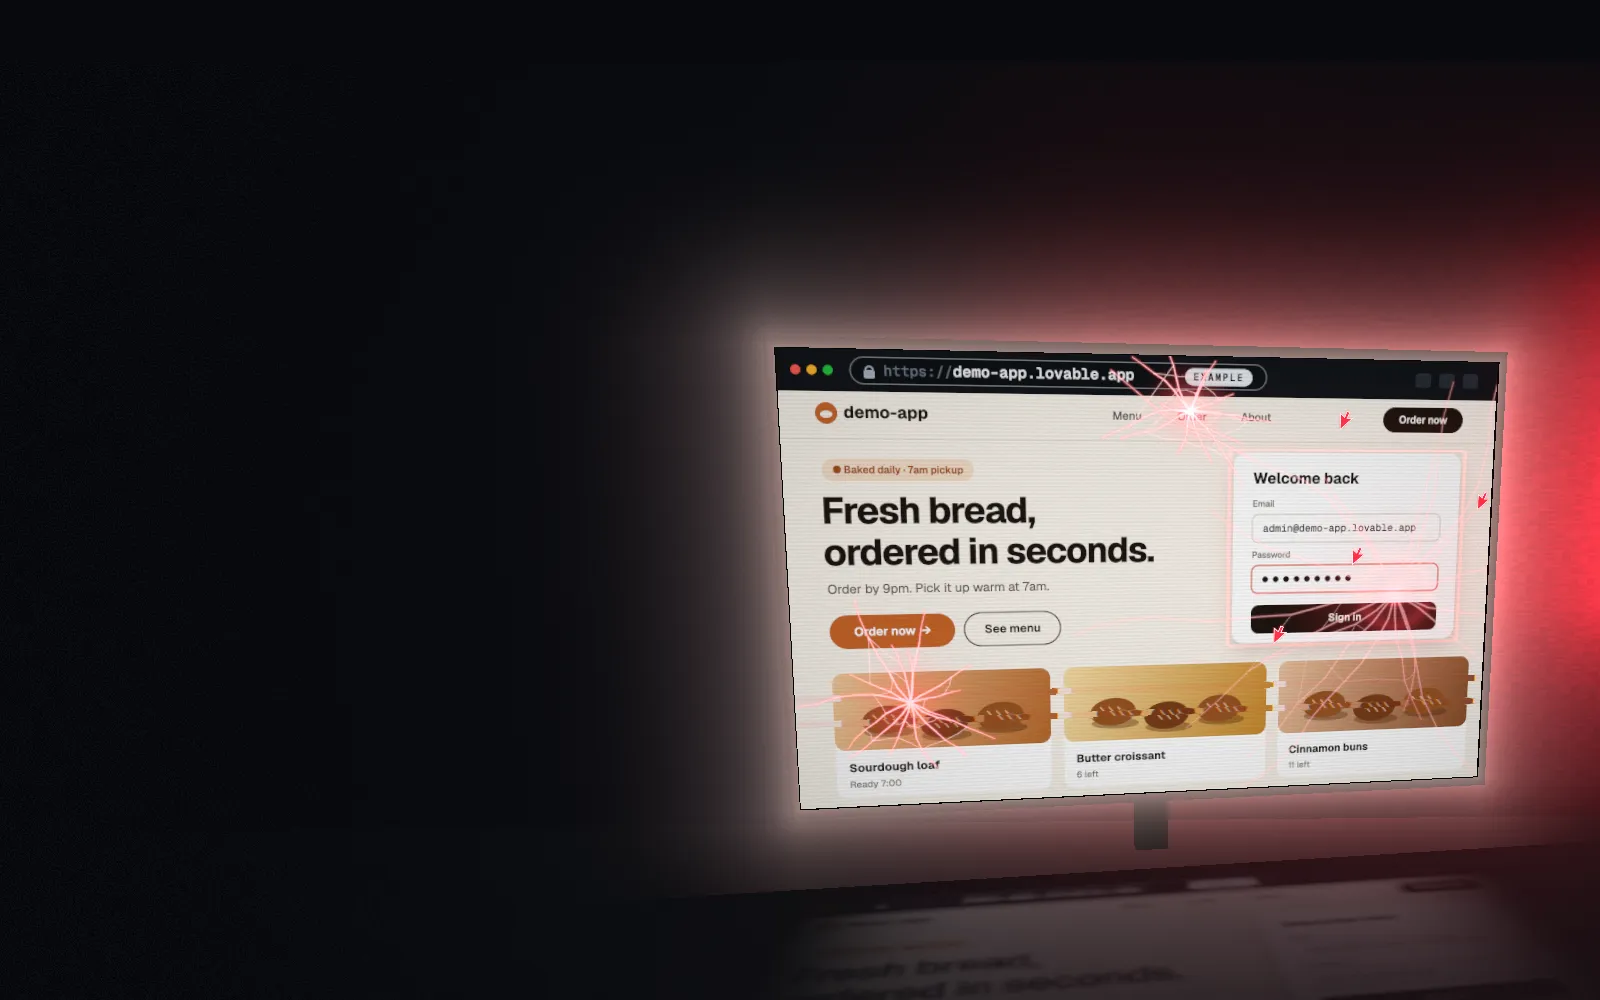
An example site under attack: bots try its .env file, its .git folder, its AI key and its database.

The next day

Then the bill comes. Then the leak.If it leaks, it's your business's name.

A stranger uses your AI key and you pay for it. Your users' emails and phone numbers get out. Your users, or your client, hear it from someone else.Your customers' names, phone numbers and notes could be open to anyone. When data leaks, people blame the business, not the builder.

  • 1 in 10apps on Lovable's showcase let anyone read or change their users' data (security researchers, 2025). Superblocks4
  • ≈1 minfor a leaked key to be found and abused, in a security test. Comparitech5
  • When users' data leaks, the lawsuits name the business. One app faced about 10 lawsuits within two weeks (2025). NBC News6
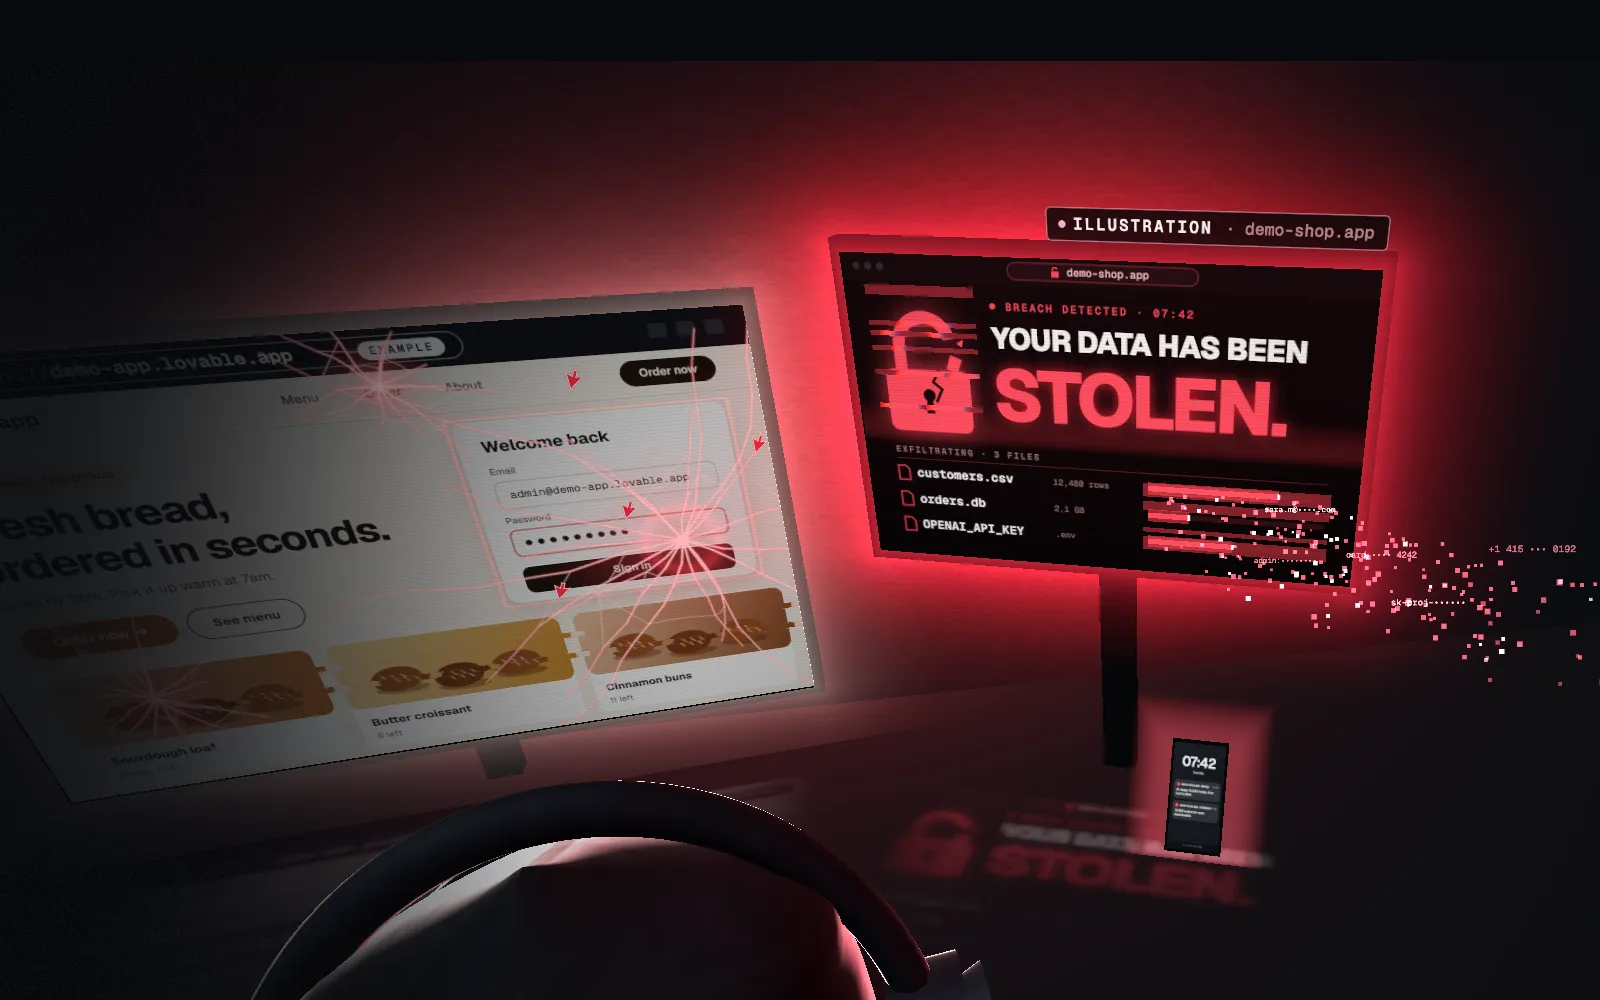
The hacker's second screen: "Your data has been stolen" on an example shop, while a phone lights up with alerts.

Today, before they do

We check it first. In about a minute.

Paste your link. We look at your app the way a hacker's tools would, and tell you what we found in plain English. Nothing gets changed.

Check my app freeCheck it free

Free check
everything a stranger can see from outside: leaked keys, exposed files, weak settings. Every problem comes with its fix.
Deep check $29
proves the app is yours, then tests whether strangers can get in: database, file storage, AI features, API.
Sample reportrecipe-pal.lovable.app

Your OpenAI key is in a file every visitor downloads.

  1. Fix nowAnyone can use your OpenAI key, and you pay./assets/index-4f2a.js · sk-proj-••••Xa9Q
  2. Fix soonAnyone can download your app's code history.GET /.git/HEAD → 200
  3. OKYour passwords file is not public.GET /.env → 404
  4. Not in the free checkThe free check can't see inside your database. The deep check ($29) can.

A sample for a made-up app. Your report shows only what we find on yours.
Our yellow scan line passes over the example site and marks each spot: locked, found, or deep check only.

The fix

Copy one prompt. Your AI fixes it.Send the report to your builder.

You get a grade and a fix for every problem we find, as one prompt for Lovable, Cursor, Claude Code or Codex. Paste it, and your AI fixes them.Every problem comes with the fix, written for them. Pay the final amount when the red items are gone.

DBafter one paste, in the sample app

fix-security.md Sample
# Fix the security problems in recipe-pal.lovable.app

You are working on my app (Vite + React, Supabase backend).
A Secure Vibes scan found the problems below. Fix them in order.

## Task 1 — Move the OpenAI call off the browser (critical)
Evidence: `sk-proj-…Xa9Q` is inside /assets/index-4f2a.js,
a file every visitor downloads.
Steps:
1. Create a Supabase Edge Function `chat` that reads
   OPENAI_API_KEY from Supabase secrets.
See the whole prompt
2. Replace the browser call to api.openai.com with a call
   to that function.
3. Remove VITE_OPENAI_API_KEY from .env and from the code.
Check: search the built files in dist/ for "sk-" → nothing.

## Task 2 — Stop publishing your .git folder (high)
Evidence: GET /.git/HEAD answers with your branch name,
so your whole code history can be downloaded.
Steps:
1. Make sure the deploy publishes only the built dist/
   folder, not the project root.
2. If your host serves the project root, add a rule that
   answers 404 for /.git/ and everything under it.
Check: open /.git/HEAD on your live site → 404.

## Guardrails (for every task)
- Do not delete data or change existing user records.
- Never paste real keys into code, comments or chat.
- After each task, run the app and make sure it still loads.

## Only you (the human) can do this
- Make a new OpenAI key at platform.openai.com/api-keys and
  delete the old one. It has been public, so treat it as stolen.

Plain Markdown. Paste it as-is into your AI.

Deep check ($29): also tests whether strangers can get into your database, file storage, AI features and API, with evidence and a fix file for every problem.Does the app store health, payment or children's data? Also have a security expert review it.

The cracks heal, the hacker's screen says Access denied, and he leans back.

Send your client proof, or check an app someone built for you

I built it

Hand it over with proof, not a promise.

Fix what we find, verify the app, then send your client a signed link: what passed, and on what date. Valid for 30 days.

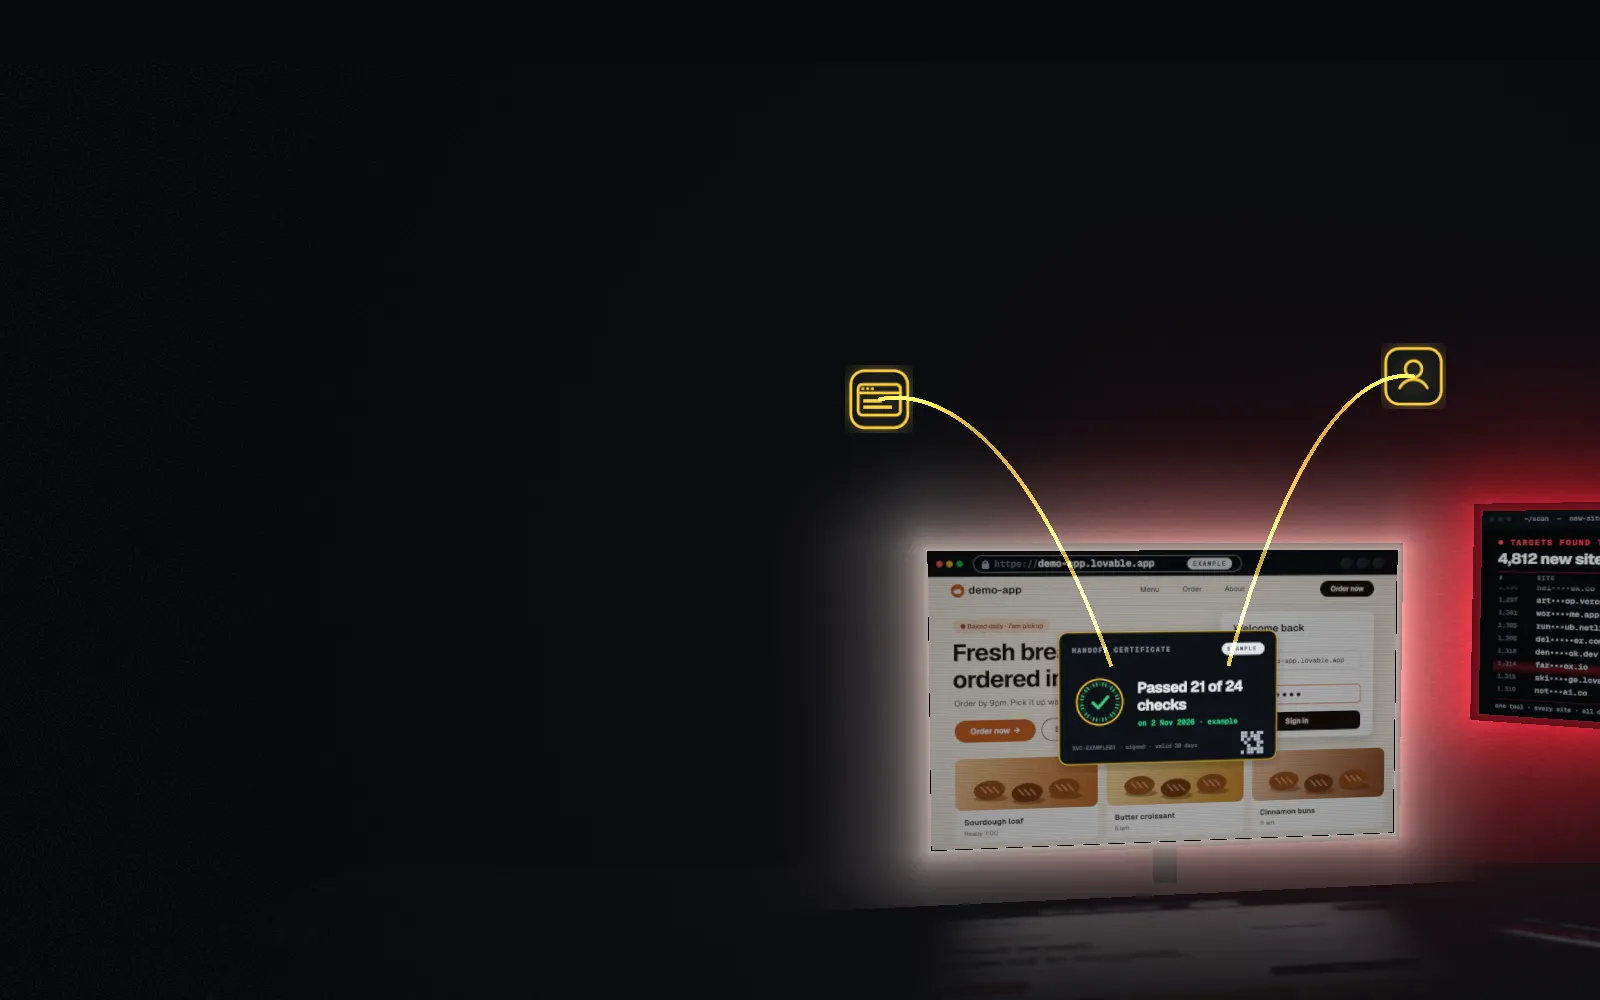
Passed 21 of 24 checkson 1 Nov 2026 · example

Issued only after you prove the app is yours and it has no serious problems left. Never says "100% secure".

Get my handoff certificate

Someone built it for me

Check it yourself, free.

Check the app yourself. You don't need anything from your builder. If they sent you a Secure Vibes link, compare the two.

Check it free
A certificate on the screen: passed 21 of 24 checks, with arcs to your client and to an app built for you.

Your turn

Check your app before a hacker does.Check it before you pay.

Free. Fixes you can paste into your AI today.Free. A plain-English report you can send your builder.

Check my app freeCheck it freeSomeone built it for me →Built it yourself? →

Your own site on the screen again, calm. The hacker has moved on.
Skip to pricing ↓

Pricing

Start free. $29 for the deep check.

The free outside check shows everything a stranger can see, with the fix for every problem. The deep check proves the app is yours, then tests whether strangers can get in. Outside re-checks are always free.

Outside check

Free just your email

Everything a stranger can see from outside.

  • Every problem with its fix, not just the worst one
  • Your grade in plain English, in about a minute
  • A clear "Not tested yet" list for what needs the deep check
  • A short video that explains your report
  • Free re-checks after you fix
Check my app free

About a minute. No code needed.

Deep check + certificate

$49 per app

For freelancers who hand apps to clients.

  • Everything in the deep check
  • A signed client certificate with a serial number
  • A QR code and a verify page your client can open
  • Valid 30 days. Never says "100% secure"
Get the certificate

Issued only when no serious problems are left.

We fix it for you

Quote after a call

We meet online, look at your app and its code together, then send a quote. Nothing is fixed or charged until you say yes.

Get in touch

Every app is different, so we price it after we've seen the code.

Someone built it for you?

Free. Check the app yourself. You don't need anything from your builder.

Check it free

Only check apps you own or have permission to check. This is not a full hacker test (penetration test). A good grade is a snapshot on a date, not a guarantee.7

FAQ

Questions people ask.

Short answers in plain words.

Who would even hack my little app?

Nobody has to choose you. Hackers' tools try every app they can find, big or small, all day. A leaked key or an open database is worth the same to them either way.

Does the free check look at my customers' data?

No. It looks at everything a stranger can see from outside. Whether strangers can open your database is tested in the deep check ($29), after you prove the app is yours. If your app stores health, payment or children's data, also have a security expert review it.

Will your check break my app or mess up my database?

No. The free check looks at what any visitor's browser already downloads, plus public records, plus a few well-known file addresses like /.env and /.git (we read the first 4 KB only and keep no values). We never log in, never send attacks and never change anything.

I built it on Lovable (or Bolt / Replit). Doesn't it already check security?

Some platforms run their own scan, and that's good. We're a second, independent check of the live app, the same for every platform. Your client can re-run it themselves.

Can I check an app someone built for me?

Yes. If it was built for your business, you can check it, also before the final payment. If you're unsure, ask the builder to say OK in writing. If they sent you a Secure Vibes certificate link, compare it with your own check.

I'm not technical. Will I understand the report?

Yes. You get a grade, a short video, and plain sentences like "anyone can use your OpenAI key". The fix is a prompt you paste into your AI. No code reading needed.

Can you fix it for me?

Yes, if you'd rather not touch anything. Get in touch and we'll set up a short online call. We go through your app and its code with you, agree on what needs doing, and send you a quote. Nothing is fixed or charged until you say yes. Every app is different, so we can only give a price after we've looked.

More questions
If I get an A, is my app hack-proof?

No one can promise that. An A means you passed the checks hackers run most, on that date. For payments or health data, also get a full review by a person.

Why do you need my email?

So only you see your report, and so we have a record that you're allowed to check this app.

What does the deep check get me that the free check doesn't?

The free check already shows every problem a stranger can see from outside, with its fix. The deep check ($29) first asks you to prove the app is yours, then tests whether strangers can get in: your database, file storage, AI features and API. Every problem comes with evidence and a fix file, plus 1 free re-check within 7 days.

Is it legal to check a site?

Yes, if it's your site, or you have the owner's permission. We ask you to confirm before every check. You sign in with a verified email and confirm, in a short statement, that you own the site or are allowed to check it. We keep a record of who checked what and when. Checking sites without permission is against our Acceptable Use Policy, and we block accounts that do it.

The free check looks only at public information a normal visitor sees. The deep-check tests run only after you also prove you control the site, with a line on your homepage, a small file, or a setting where you bought your web address.

What do you store?

Your report: the problems we found and where. Any key we find is cut down to its first and last 4 characters before it's saved. If your database is open, we record table names and row counts, never the rows themselves. We also keep your email address, which version of our Terms you accepted, and for every check a record of who asked for it, the site, the time and the statement you confirmed. Reports are private to your account and auto-delete after 90 days. We keep a scrambled, one-way version of your IP address for rate limiting and abuse prevention. Details are in our Privacy Policy.

How do I prove the app is mine?

Pick one: paste a prompt we give you into your AI (it adds one line to your homepage), upload a one-line text file, or add a setting where you bought your link. We check automatically. It takes about a minute.

Which AI tools does the prompt work with?

Claude Code, Codex, Cursor, Lovable, Antigravity, Bolt, Replit Agent, Windsurf: anything that takes a Markdown instruction. Pick yours on the report page and the prompt adjusts its wording.

Sources & fine print

  1. "Within minutes" and "they try every site": Kondracki et al., Uninvited Guests, USENIX Security 2022 (4,657 new websites drew 1.5M requests from 31,898 addresses; 105 malicious campaigns), and HUMAN Security (2025). It applies most to apps on their own domain; apps on shared platform addresses are often found other ways, such as search engines and showcases.
  2. SANS ISC, "Survival time for web sites", 29 Aug 2023: one new site with its own certificate. The first automated visitor arrived about a second after the certificate appeared in the public log; requests for /.env, /.git/config, /.DS_Store, /config.json, /.vscode/sftp.json and /server-status followed within about two seconds. One site, not an average. The hero's request log replays those paths (plus the files our free check asks for); it is not traffic to your app.
  3. Palo Alto Unit 42, large-scale cloud extortion operation, 15 Aug 2024: .env files copied from at least 110,000 domains by an automated operation.
  4. CVE-2025-48757 (Superblocks write-up): 170 of 1,645 Lovable showcase apps, May 2025. Fixed per app; the platform has changed since.
  5. Comparitech GitHub honeypot: a cloud key leaked on GitHub, abused within about 1 minute. A key in a code repository, not inside a website.
  6. Tea app: about 10 lawsuits reported by early August 2025 (NBC News). Tea is not known to be AI-built.
  7. Our check: the free check is look-only. The deep check needs proof that the app is yours. It is not a full hacker test (penetration test). A good grade is a snapshot on a date, not a guarantee. The hackers, doors and leaks on this page are an illustration, not a scan of your app.

Hackers try every new app.Before you pay, check it.

Check mine freeCheck it free